| ID |
Date |
Author |
Topic |
Subject |
|
483
|
28 May 2008 |
Konstantin Olchanski | Bug Report | pending problems and fixes from triumf | > Here is the list of known problems I am aware of and of fixes not yet committed
> to midas svn:
>
> 1) added variable /equiment/foo/common/PerVariableHistory
corrected in svn revision 4203, read
http://savannah.psi.ch/viewcvs/trunk/src/mlogger.c?root=midas&rev=4203&sortby=rev&view=log
> 2) writing compressed midas files (foo.mid.gz) crashes the mlogger when file
> size reaches 2 GBytes. This problem could be new in SL5.1.
(no change)
> 3) when a midas client becomes unresponsive, runs cannot be stopped using the
> "stop" button in mhttpd. This is because cm_transition() loops over all attached
> clients, but never removes clients that are known to be dead. Proposed fix is to
> call cm_check_client() for each client before calling their rpc transition handler.
Fixed in SVN revision 4198, read
http://savannah.psi.ch/viewcvs/trunk/src/midas.c?root=midas&rev=4201&sortby=rev&view=log
> 4) the discussed before fix for reading broken history files (skip bad data).
Fixed in SVN revision 4202, read https://ladd00.triumf.ca/elog/Midas/482
> 5) mhttpd history "export" button needs to be fixed (by request from ALPHA). At
> present it either does not return all exiting data or crashes mhttpd. (no fix)
(no change)
> 6) mhttpd ODB editor in "set value" page, the "cancel" button is broken (needs
> to be corrected for "relative URL").
Apply this patch to src/mhttpd.c
@@ -11156,10 +11190,7 @@
sprintf(str, "SC/%s/%s", eq_name, group);
redirect(str);
} else {
- strlcpy(str, path, sizeof(str));
- if (strrchr(str, '/'))
- strlcpy(str, strrchr(str, '/')+1, sizeof(str));
- redirect(str);
+ redirect("./");
}
> 7) mhttpd needs AJAX-style methods for reading and writing ODB. (no fix)
(no change)
K.O. |
|
484
|
29 May 2008 |
Konstantin Olchanski | Bug Report | pending problems and fixes from triumf | > > Here is the list of known problems I am aware of and of fixes not yet committed to midas svn:
> > 1) added variable /equiment/foo/common/PerVariableHistory
>
> corrected in svn revision 4203, read
> http://savannah.psi.ch/viewcvs/trunk/src/mlogger.c?root=midas&rev=4203&sortby=rev&view=log
Was still broken - all should work in revision 4207.
> > 2) writing compressed midas files (foo.mid.gz) crashes the mlogger when file
> > size reaches 2 GBytes. This problem could be new in SL5.1.
It turns out that on SL5 and SL5.1 (and others?) the 32-bit version of ZLIB opens the
compressed output file without the O_LARGEFILE flag, this limits the file size to 2 GB.
Fixed by opening the file ourselves, then attach compression stream using gzdopen().
Revision 4207. (Not tested on Windows - may be broken!)
> > 5) mhttpd history "export" button needs to be fixed (by request from ALPHA). At
> > present it either does not return all exiting data or crashes mhttpd. (no fix)
>
> (no change)
>
> > 6) mhttpd ODB editor in "set value" page, the "cancel" button is broken (needs
> > to be corrected for "relative URL").
>
> Apply this patch to src/mhttpd.c
>
> @@ -11156,10 +11190,7 @@
> sprintf(str, "SC/%s/%s", eq_name, group);
> redirect(str);
> } else {
> - strlcpy(str, path, sizeof(str));
> - if (strrchr(str, '/'))
> - strlcpy(str, strrchr(str, '/')+1, sizeof(str));
> - redirect(str);
> + redirect("./");
> }
>
> > 7) mhttpd needs AJAX-style methods for reading and writing ODB. (no fix)
>
> (no change)
>
> K.O. |
|
1179
|
17 May 2016 |
Konstantin Olchanski | Info | openssl situation, MacOS 10.11 (El Capitan) openssl compilation errors | > I recently upgraded my macbook to MacOS 10.11.
> [ and midas would not compile ]
> It seems that MacOS has now fully removed openssl ...
My read of tea leaves - the macos version of openssl was so old it was almost useless, did not support any of the modern HTTPS
features. So to use mhttpd with https you pretty much had to install openssl from macports anyway. For macos 10.11 maybe they
looked at upgrading to newer version, but since the openssl kerfuffle last year, there is several forks of openssl (the OpenBSD fork
named libressl is the best, IMO), so rather than picking and choosing, they deleted the whole thing.
Now back to MIDAS.
We use the mongoose web server module and I have expected by now for them to make a move on improving HTTPS support, but no
move happened.
Right now mongoose support OpenSSL only (I would expect the OpenBSD LibreSSL fork to work to of the box, too). Other then that,
they have:
a) their own mickey-mouse https library (krypton) which does not support any modern cryptography (RC4 only - when RC4 is known to
be useless).
b) an adapter library (polar) for interfacing with PolarSSL (mbedtls)
At this point I would rather abandon the implicit dependency on the system-provided openssl and have an explicit dependancy on a
modern https crypto library.
Option (b) would work for us -
1) add "git clone mbedtls; cd mbedtls; make" to midas build instructions
2) add polarssl_compat.c to midas git (from cessanta/polar repo)
3) retest mhttpd against ssllabs https scanner, retest against all web browsers.
The downside of this route is loss of automatic nightly updates to the https crypto library (for better or for worse).
K.O.
P.S. Because on MacOS use of openssl from macports is pretty much required, it should be moved from the "tricks" page to the
standard midas installation instructions ("install required packages"). |
|
2736
|
15 Apr 2024 |
Konstantin Olchanski | Bug Report | open MIDAS RPC ports | we had a bit of trouble with open network ports recently and I now think security of MIDAS RPC
ports needs to be tightened.
TL;DR, this is a non-trivial network configuration problem, TL required, DR up to you.
as background, right now we have two settings in ODB, "/expt/security/enable non-localhost
RPC" set to "no" (the default) and set to "yes". Set to "no" is very secure, all RPC sockets
listen only on the "localhost" interface (127.0.0.1) and do not accept connections from other
computers. Set to "yes", RPC sockets accept connections from everywhere in the world, but
immediately close them without reading any data unless connection origins are listed in ODB
"/expt/security/RPC hosts" (white-listed).
the problem, one. for security and robustness we place most equipments on a private network
(192.168.1.x). MIDAS frontends running on these equipments must connect to MIDAS running on
the main computer. This requires setting "enable non-localhost RPC" to "yes" and white-listing
all private network equipments. so far so good.
the problem, one, continued. in this configuration, the MIDAS main computer is usually also
the network gateway (with NAT, IP forwarding, DHCP, DNS, etc). so now MIDAS RPC ports are open
to all external connections (in the absence of restrictive firewall rules). one would hope for
security-through-obscurity and expect that "external threat actors" will try to bother them,
but in reality we eventually see large numbers of rejected unwanted connections logged in
midas.log (we log the first 10 rejected connections to help with maintaining the RPC
connections white-list).
the problem, two. central IT do not like open network ports. they run their scanners, discover
the MIDAS RPC ports, complain about them, require lengthy explanations, etc.
it would be much better if in the typical configuration, MIDAS RPC ports did not listen on
external interfaces (campus network). only listen on localhost and on private network
interfaces (192.168.1.x).
I am not yet of the simplest way to implement this. But I think this is the direction we
should go.
P.S. what about firewall rules? two problems: one: from statistic-of-one, I make mistakes
writing firewall rules, others also will make mistakes, a literally fool-proof protection of
MIDAS RPC ports is needed. two: RHEL-derived Linuxes by-default have restrictive firewall
rules, and this is good for security, except that there is a failure mode where at boot time
something can go wrong and firewall rules are not loaded at all. we have seen this happen.
this is a complete disaster on a system that depends on firewall rules for security. better to
have secure applications (TCP ports protected by design and by app internals) with firewall
rules providing a secondary layer of protection.
P.P.S. what about MIDAS frontend initial connection to the mserver? this is currently very
insecure, but the vulnerability window is very small. Ideally we should rework the mserver
connection to make it simpler, more secure and compatible with SSH tunneling.
P.P.S. Typical network diagram:
internet - campus firewall - campus network - MIDAS host (MIDAS) - 192.168.1.x network - power
supplies, digitizers, MIDAS frontends.
P.P.S. mserver connection sequence:
1) midas frontend opens 3 tcp sockets, connections permitted from anywhere
2) midas frontend opens tcp socket to main mserver, sends port numbers of the 3 tcp sockets
3) main mserver forks out a secondary (per-client) mserver
4) secondary mserver connects to the 3 tcp sockets of the midas frontend created in (1)
5) from here midas rpc works
6) midas frontend loads the RPC white-list
7) from here MIDAS RPC sockets are secure (protected by the white-list).
(the 3 sockets are: RPC recv_sock, RPC send_sock and event_sock)
P.P.S. MIDAS UDP sockets used for event buffer and odb notifications are secure, they bind to
localhost interface and do not accept external connections.
K.O. |
|
2737
|
16 Apr 2024 |
Stefan Ritt | Bug Report | open MIDAS RPC ports | One thing coming to my mind is the interface binding. If you have a midas host with two networks
("global" and "local"=192.168.x.x), you can tell to which interface a socket should bind.
By default it binds both interfaces, but we could restrict the socket only to bind to the local
interface 192.168.x.x. This way the open port would be invisible from the outside, but from
your local network everybody can connect easily without the need of a white list.
Stefan |
|
676
|
26 Nov 2009 |
Konstantin Olchanski | Bug Report | once in 100 years midas shared memory bug | We were debugging a strange problem in the event builder, where out of 14
fragments, two fragments were always getting serial number mismatches and the
serial numbers were not sequentially increasing (the other 12 fragments were
just fine).
Then we noticed in the event builder debug output that these 2 fragments were
getting assigned the same buffer handle number, despite having different names -
BUF09 and BUFTPC.
Then we looked at "ipcs", counted the buffers, and there are only 13 buffers for
14 frontends.
Aha, we went, maybe we have unlucky buffer names, renamed BUFTPC to BUFAAA and
everything started to work just fine.
It turns out that the MIDAS ss_shm_open() function uses "ftok" to convert buffer
names to SystemV shared memory keys. This "ftok" function promises to create
unique keys, but I guess, just not today.
Using a short test program, I confirmed that indeed we have unlucky buffer names
and ftok() returns duplicate keys, see below.
Apparently ftok() uses the low 16 bits of the file inode number, but in our
case, the files are NFS mounted and inode numbers are faked inside NFS. When I
run my test program on a different computer, I get non-duplicate keys. So I
guess we are double unlucky.
Test program:
#include <stdio.h>
#include <sys/types.h>
#include <sys/ipc.h>
int main(int argc, char* argv[])
{
//key_t ftok(const char *pathname, int proj_id);
int k1 = ftok("/home/t2kdaq/midas/nd280/backend/.BUF09.SHM", 'M');
int k2 = ftok("/home/t2kdaq/midas/nd280/backend/.BUFTPC.SHM", 'M');
int k3 = ftok("/home/t2kdaq/midas/nd280/backend/.BUFFGD.SHM", 'M');
printf("key1: 0x%08x, key2: 0x%08x, key3: 0x%08x\n", k1, k2, k3);
return 0;
}
[t2kfgd@t2knd280logger ~/xxx]$ g++ -o ftok -Wall ftok.cxx
[t2kfgd@t2knd280logger ~/xxx]$ ./ftok
key1: 0x4d138154, key2: 0x4d138154, key3: 0x4d138152
Also:
[t2kfgd@t2knd280logger ~/xxx]$ ls -li ...
14385492 -rw-r--r-- 1 t2kdaq t2kdaq 8405052 Nov 24 17:42
/home/t2kdaq/midas/nd280/backend/.BUF09.SHM
36077906 -rw-r--r-- 1 t2kdaq t2kdaq 67125308 Nov 26 10:19
/home/t2kdaq/midas/nd280/backend/.BUFFGD.SHM
36077908 -rw-r--r-- 1 t2kdaq t2kdaq 8405052 Nov 25 15:53
/home/t2kdaq/midas/nd280/backend/.BUFTPC.SHM
(hint: print the inode numbers in hex and compare to shm keys printed by the
program)
K.O. |
|
3200
|
05 Feb 2026 |
Konstantin Olchanski | Bug Report | omnibus bugs from running DarkLight | We finished running the DarkLight experiment and I am reporting accumulated bugs that we have run into.
1) history plots on 12 hrs, 24 hrs tend to hang with "page not responsive". most plots have 16-20 variables,
which are recorded at 1/sec interval. (yes, we must see all the variables at the same time and yes, we want to
record them with fine granularity).
2) starting runs gets into a funny mode if a GEM frontend aborts (hardware problems), transition page reports
"wwrrr, timeout 0", and stays stuck forever, "cancel transition" does nothing. observe it goes from "w"
(waiting) to "r" (RPC running) without a "c" (connecting...) and timeout should never be zero (120 sec in
ODB).
3) ODB editor clicking on hex number versus decimal number no longer allows editing in hex, Stefan implemented
this useful feature and it worked for a while, but now seems broken.
4) ODB editor "right click" to "delete" or "rename" key does not work, the right-click menu disappears
immediately before I can use it (dl-server-2), click on item (it is now blue), right-click menu disappears
before I can use it (daq17). it looks like a timing or race condition.
5) ODB editor "create link" link target name is limited to 32 bytes, links cannot be created (dl-server-2), ok
on daq17 with current MIDAS.
6) MIDAS on dl-server-2 is "installed" in such a way that there is no connection to the git repository, no way
to tell what git checkout it corresponds to. Help page just says "branch master", git-revision.h is empty. We
should discourage such use of MIDAS and promote our "normal way" where for all MIDAS binary programs we know
what source code and what git commit was used to build them.
6a) MIDAS on dl-server-2 had a pretty much non-functional history display, I reported it here, Stefan provided
a fix, I manually retrofitted it into dl-server-2 MIDAS and we were able to run the experiment. (good)
6b) bug (5) suggests that there is more bugs being introduced and fixed without any notice to other midas
users (via this forum or via the bitbucket bug tracker).
K.O. |
|
3201
|
06 Feb 2026 |
Stefan Ritt | Bug Report | omnibus bugs from running DarkLight | Thanks for the detailed report. Let me reply one-by-one.
> 1) history plots on 12 hrs, 24 hrs tend to hang with "page not responsive". most plots have 16-20 variables,
> which are recorded at 1/sec interval. (yes, we must see all the variables at the same time and yes, we want to
> record them with fine granularity).
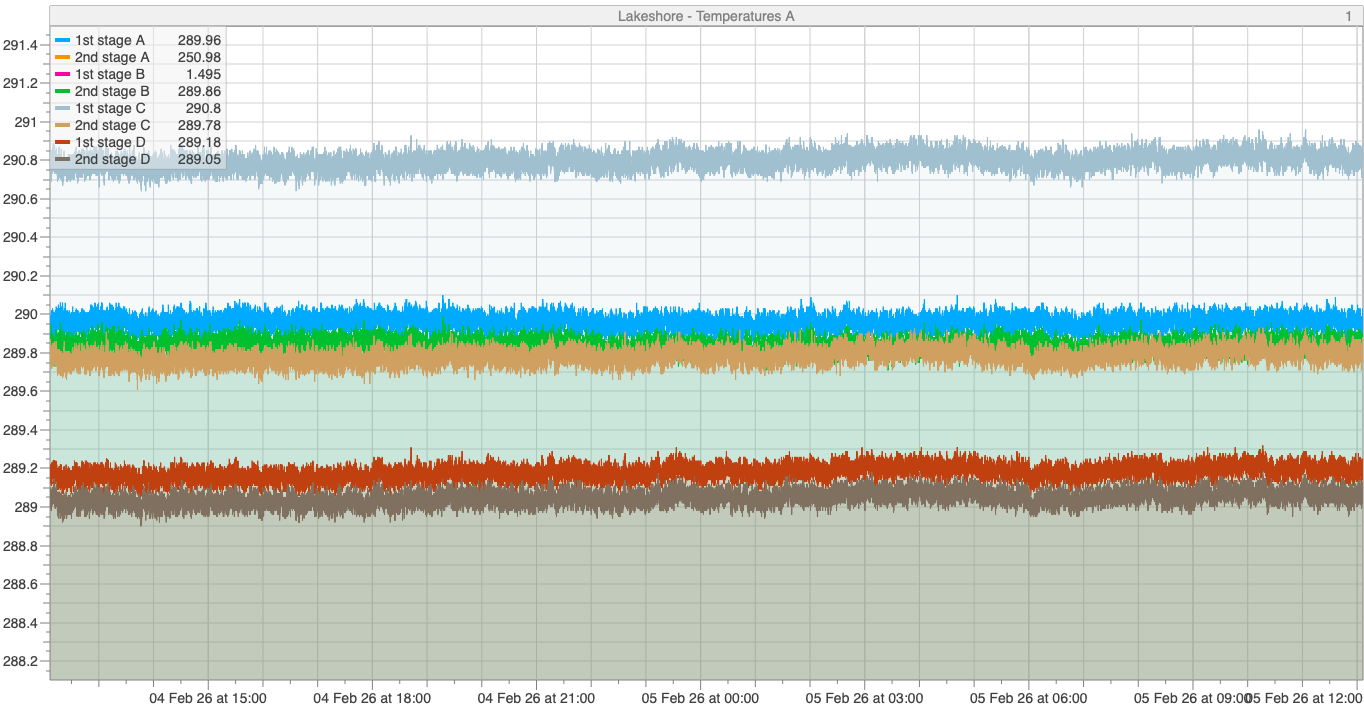
Attached is a similar plot. 8 values recorded every second, displayed for 24h. The backend is actually a Raspberry Pi! I see no issues there. Do you have
the current history version which does the re-binning? Actually the plot below is still without rebinding (see the "1" at the top right), and it contains ~72000 points x 8. The browser does not have any issue
with it.
Stefan |
| Attachment 1: Lakeshore-Temperatures_A-20260204-120628-20260205-120628.png
|
|
|
3202
|
06 Feb 2026 |
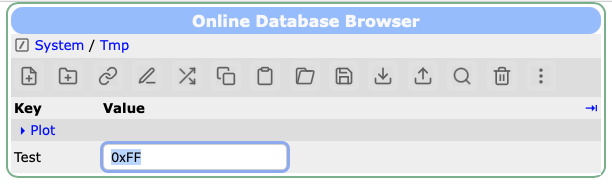
Stefan Ritt | Bug Report | omnibus bugs from running DarkLight | > 3) ODB editor clicking on hex number versus decimal number no longer allows editing in hex, Stefan implemented
> this useful feature and it worked for a while, but now seems broken.
I cannot confirm. See below. There was some issue some time ago, but that's fixed since a while. Please pull on develop and try again.
Here is the change: https://bitbucket.org/tmidas/midas/commits/882974260876529c43811c63a16b4a32395d416a
Stefan |
| Attachment 1: Screenshot_2026-02-06_at_12.44.16.png
|
|
|
3203
|
06 Feb 2026 |
Stefan Ritt | Bug Report | omnibus bugs from running DarkLight | > 4) ODB editor "right click" to "delete" or "rename" key does not work, the right-click menu disappears
> immediately before I can use it (dl-server-2), click on item (it is now blue), right-click menu disappears
> before I can use it (daq17). it looks like a timing or race condition.
Confirmed and fixed: https://bitbucket.org/tmidas/midas/commits/4ba30761683ac9aa558471d2d2d35ce05e72096a
/Stefan |
|
3204
|
06 Feb 2026 |
Stefan Ritt | Bug Report | omnibus bugs from running DarkLight | > 5) ODB editor "create link" link target name is limited to 32 bytes, links cannot be created (dl-server-2), ok
> on daq17 with current MIDAS.
Works for me with the current version.
> 6) MIDAS on dl-server-2 is "installed" in such a way that there is no connection to the git repository, no way
> to tell what git checkout it corresponds to. Help page just says "branch master", git-revision.h is empty. We
> should discourage such use of MIDAS and promote our "normal way" where for all MIDAS binary programs we know
> what source code and what git commit was used to build them.
Not sure if you have seen it. I make a "install" script to clone, compile and install midas. Some people use this already. Maybe give it a shot. Might need
adjustment for different systems, I certainly haven't covered all corner cases. But on a RaspberryPi it's then just one command to install midas, modify
the environment, install mhttpd as a service and load the ODB defaults. I know that some people want it "their way" and that's ok, but for the novice user
that might be a good starting point. It's documented here: https://daq00.triumf.ca/MidasWiki/index.php/Install_Script
The install script is plain shell, so should be easy to be understandable.
> 6a) MIDAS on dl-server-2 had a pretty much non-functional history display, I reported it here, Stefan provided
> a fix, I manually retrofitted it into dl-server-2 MIDAS and we were able to run the experiment. (good)
>
> 6b) bug (5) suggests that there is more bugs being introduced and fixed without any notice to other midas
> users (via this forum or via the bitbucket bug tracker).
If I would notify everybody about a new bug I introduced, I would know that it's a bug and I would not introduce it ;-)
For all the fixes I encourage people to check the commit log. Doing an elog entry for every bug fix would be considered spam by many people because
that can be many emails per week. The commit log is here: https://bitbucket.org/tmidas/midas/commits/branch/develop
If somebody volunteers to consolidate all commits and make a monthly digest to be posted here, I'm all in favor, but I'm not that individual.
Stefan |
|
3205
|
12 Feb 2026 |
Stefan Ritt | Bug Report | omnibus bugs from running DarkLight | Now I had a similar case that the browser froze when showing 24h of data. Tuned out that 80k points are a bit much. I changed the code so that it starts binning when showing 8h or more. This is not a perfect solution. The code should check at which interval data is written, then
automatically start binning when approaching 4000 points or more. That would however require more complicated code, so I leave it as it is right now. Feedback welcome.
Stefan |
|
3173
|
08 Dec 2025 |
Konstantin Olchanski | Bug Report | odbxx memory leak with JSON ODB dump | I was testing odbxx with manalyzer, decided to print an odb value in every event,
and it worked fine in online mode, but bombed out when running from a data file
(JSON ODB dump). The following code has a memory leak. No idea if XML ODB dump
has the same problem.
int memory_leak()
{
midas::odb::set_odb_source(midas::odb::STRING, std::string(run.fRunInfo-
>fBorOdbDump.data(), run.fRunInfo->fBorOdbDump.size()));
while (1) {
int time = midas::odb("/Runinfo/Start time binary");
printf("time %d\n", time);
}
}
K.O. |
|
3176
|
09 Dec 2025 |
Stefan Ritt | Bug Report | odbxx memory leak with JSON ODB dump | Thanks for reporting this. It was caused by a
MJsonNode* node = MJsonNode::Parse(str.c_str());
not followed by a
delete node;
I added that now in odb::odb_from_json_string(). Can you try again?
Stefan |
|
3179
|
09 Dec 2025 |
Konstantin Olchanski | Bug Report | odbxx memory leak with JSON ODB dump | > Thanks for reporting this. It was caused by a
>
> MJsonNode* node = MJsonNode::Parse(str.c_str());
>
> not followed by a
>
> delete node;
>
> I added that now in odb::odb_from_json_string(). Can you try again?
>
> Stefan
Close, but no cigar, node you delete is not the node you got from Parse(), see "node = subnode;".
If I delete the node returned by Parse(), I confirm the memory leak is gone.
BTW, it looks like we are parsing the whole JSON ODB dump (200k+) on every odbxx access. Can you parse it just once?
K.O. |
|
3180
|
10 Dec 2025 |
Stefan Ritt | Bug Report | odbxx memory leak with JSON ODB dump | > BTW, it looks like we are parsing the whole JSON ODB dump (200k+) on every odbxx access. Can you parse it just once?
You are right. I changed the code so that the dump is only parsed once. Please give it a try.
Stefan |
|
3182
|
11 Dec 2025 |
Konstantin Olchanski | Bug Report | odbxx memory leak with JSON ODB dump | > > BTW, it looks like we are parsing the whole JSON ODB dump (200k+) on every odbxx access. Can you parse it just once?
> You are right. I changed the code so that the dump is only parsed once. Please give it a try.
Confirmed fixed, thanks! There are 2 small changes I made in odbxx.h, please pull.
K.O. |
|
3184
|
12 Dec 2025 |
Stefan Ritt | Bug Report | odbxx memory leak with JSON ODB dump | > Confirmed fixed, thanks! There are 2 small changes I made in odbxx.h, please pull.
There was one missing enable_jsroot in manalyzer, please pull yourself.
Stefan |
|
3185
|
12 Dec 2025 |
Konstantin Olchanski | Bug Report | odbxx memory leak with JSON ODB dump | > > Confirmed fixed, thanks! There are 2 small changes I made in odbxx.h, please pull.
> There was one missing enable_jsroot in manalyzer, please pull yourself.
pulled, pushed to rootana, thanks for fixing it!
K.O. |
|
2871
|
09 Oct 2024 |
Lukas Gerritzen | Suggestion | odbedit minor quality of life | I have made two minor quality of life changes to odbedit.
- cd command: Typing cd without arguments now changes the directory to /, similar to the behaviour of the cd command in Linux sending you to the home directory.
- Exit behavior: Upon exiting the program with Ctrl+C, a newline character is printed so that the command line starts on an empty line rather than the last line from odbedit.
Here's the diff:
@@ -1668,7 +1668,10 @@ int command_loop(char *host_name, char *exp_name, char *cmd, char *start_dir)

       /* cd */
       else if (param[0][0] == 'c' && param[0][1] == 'd') {
-         compose_name(pwd, param[1], str);
+         if (strlen(param[1]) == 0)
+            strcpy(str, "/");
+         else
+            compose_name(pwd, param[1], str);

          status = db_find_key(hDB, 0, str, &hKey);

@@ -2962,6 +2965,7 @@ void ctrlc_odbedit(INT i)

    cm_disconnect_experiment();

+   printf("\n");
    exit(EXIT_SUCCESS);
 }
Please consider incorporating those changes to odbedit.
Lukas |
|